Why Trojan
No security expertise needed
AI reads every vulnerability found by the scanners and explains it in your terms — based on how much technical knowledge you have. You don’t need to be tech-savvy to ship your ideas in peace.
Local-first
Your code never leaves your machine. No cloud uploads, no third-party access. Keep your sensitive codebase private while you scale.
Investor-ready reports
When a client or VC asks about your security posture — one click generates a professional report. Go from “we’ll get to it” to “here’s our latest scan” in seconds.
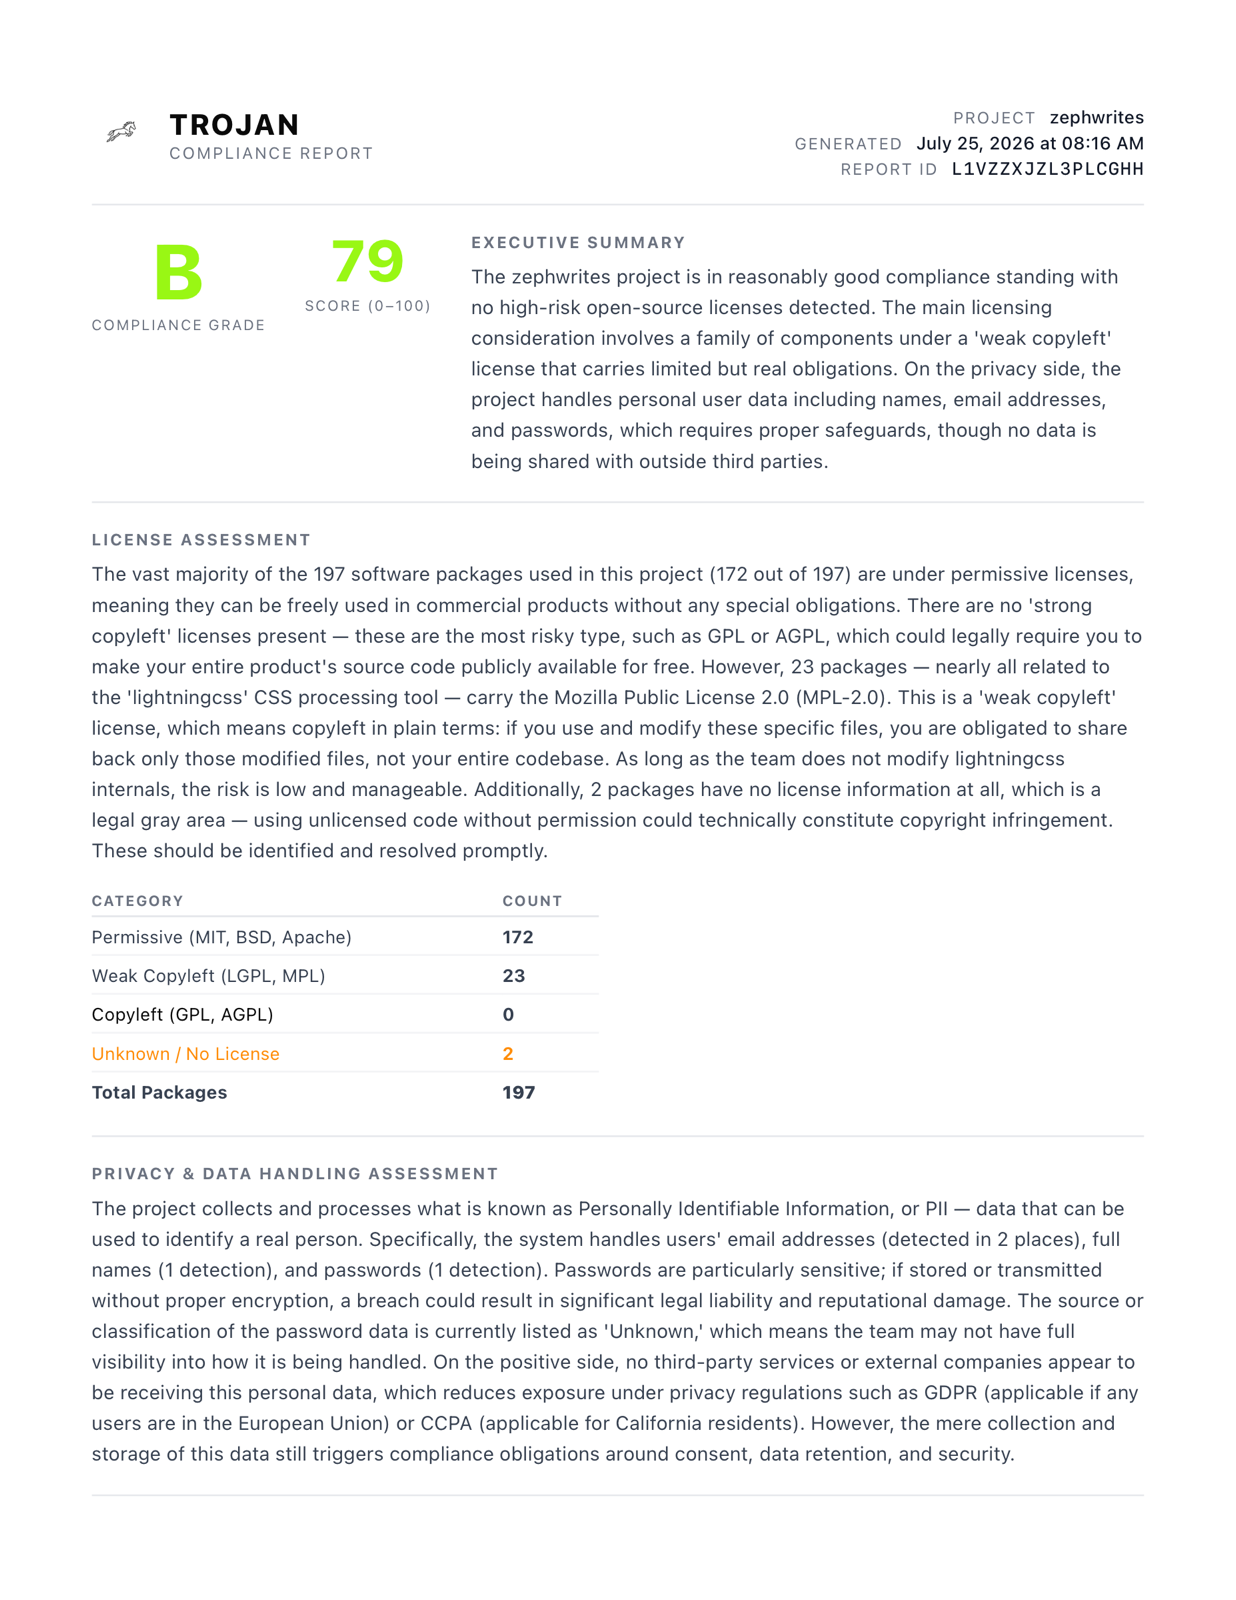
API keys, tokens and passwords committed by accident — the number-one way small teams get breached. Trojan finds them in your history, not just the latest commit.
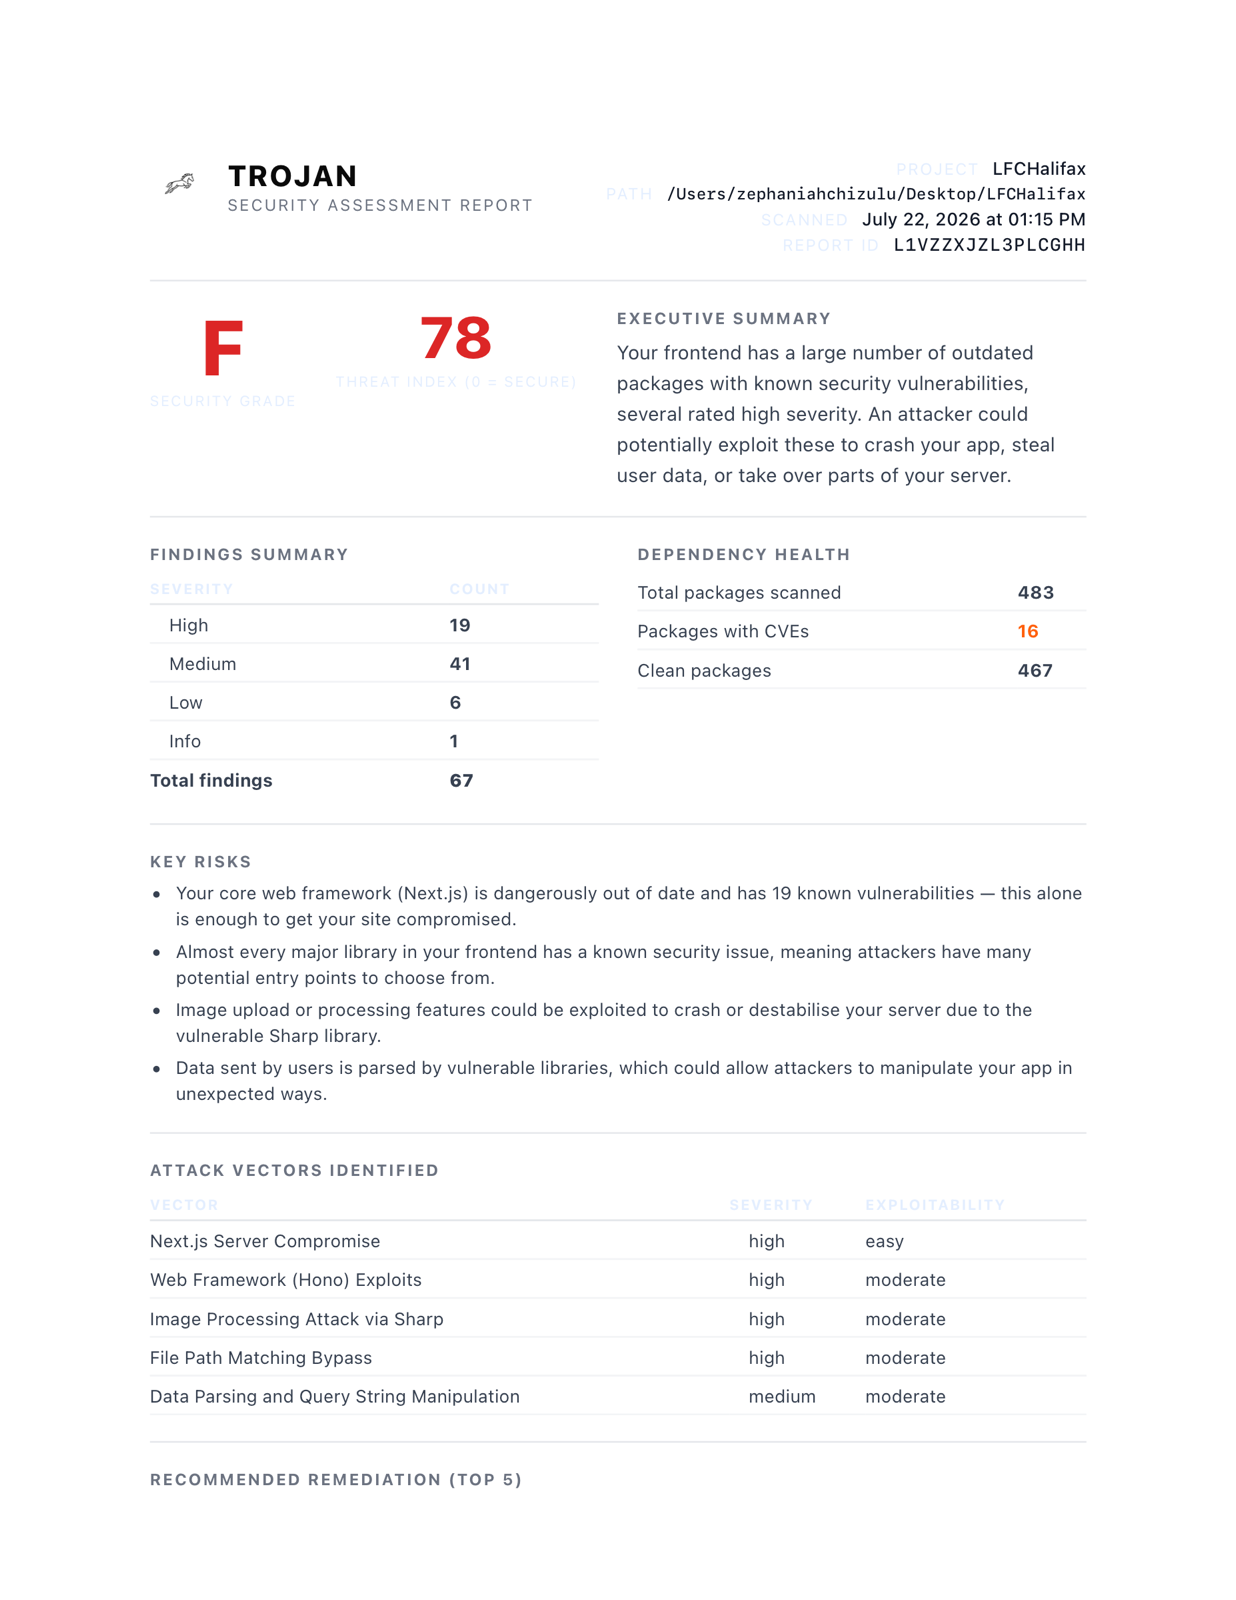
Known vulnerabilities in the open-source packages you install, matched to public advisories — with the safe version to upgrade to.
Injection, broken auth, unsafe defaults — the patterns attackers probe for first. Trojan reads intent, not just keywords.
Every finding explains the risk in words a founder can act on, and the exact change for the engineer. No CVE jargon required.
| No. | Coverage | Value | Remark |
|---|---|---|---|
| 01 | Detection rules | 3,400+ | Updated weekly from public advisories |
| 02 | Languages supported | 14 | JS/TS, Python, Go, Ruby, Rust, Java… |
| 03 | Median scan time | 4.2 s | On a 100,000-line repository |
| 04 | Code sent to our servers | 0 bytes | Scanning runs entirely on your machine |
Five levels.
Ranked, not colored.
No wall of red. Trojan sorts every finding by how likely it is to be exploited and how much it would hurt — so you always know what to do first, and when it's safe to stop.
Scanning is free. You pay for AI.
The whole scanner, unlimited. 500 tokens a month. No card required.
For one developer shipping regularly.
A small team on one bill, drawing from one token pool.